PHP Patches 2 Critical Vulnerabilities: Site Care Websites Already Upgraded
What happened?
On October 21, 2026, PHP released a fix for 2 Critical-severity vulnerabilities. Attackers could use them to run code on the server without logging in, then take over the website, inject malware or steal data.
PHP is the platform every WordPress site runs on. So these flaws are not in a single plugin or theme. They affect every website running an unpatched PHP version. Sites on PHP versions that have reached end of life (such as PHP 7.4) are at even greater risk, because they will never get a patch.
Site Care reviewed and upgraded
As soon as the patch was announced, VIG Site Care:
- Reviewed the PHP version of every client website we monitor.
- Applied the latest patch to websites on a supported PHP version.
- Upgraded websites still on old, end-of-life PHP to a current version.
- Fixed plugins that were incompatible with the new PHP version, so each site kept all the features it uses.
- Checked everything after the upgrade: main pages load normally, contact forms submit successfully for real, and submissions reach the right email inbox and customer management system.
Every change was backed up before it was made.
Websites managed by Site Care are safe
Websites handled by Site Care are no longer affected by these 2 vulnerabilities. Site Care keeps checking PHP versions every day and alerts you as soon as a new patch is out.
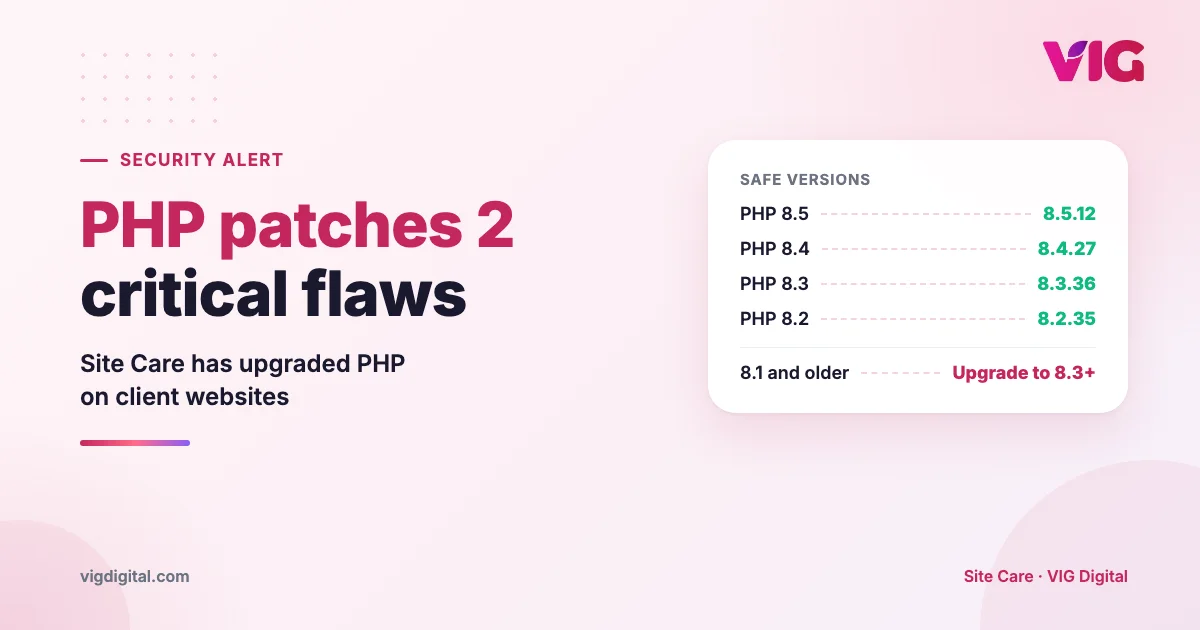
If your website is not monitored yet, check your PHP version now: in the WordPress admin, go to Tools → Site Health → Info → Server. Safe versions: 8.5.12, 8.4.27, 8.3.36 or 8.2.35 and later.
Site Care checks your website's PHP, WordPress and plugin versions every day, alerts you as soon as a new vulnerability appears, and sends a report every Monday.
Source: php.net security announcement, October 21, 2026.